Cloud Incident Response Automation on AWS
Abstract: Automating cloud incident response workflows using AWS services for real-time detection, response, and mitigation of security incidents.
OverviewFaster than a human on call
This project centers on the automation of security incident response within the AWS cloud environment by leveraging key AWS services, including GuardDuty, Lambda, EventBridge, SNS, CloudTrail, and CloudWatch. The primary objective is to overcome the limitations of traditional manual response methods, which are often too slow and inconsistent to effectively mitigate security threats in dynamic cloud infrastructures.
By integrating these AWS services, the system is designed to detect potential threats in real time, analyze them, and automatically trigger predefined response actions such as isolating compromised EC2 instances and notifying security stakeholders. This automated approach not only reduces response times but also ensures consistency, scalability, and improved operational efficiency in incident management. The project highlights how coordinated service orchestration can enhance an organization's overall security posture in a cloud-native environment.
ArchitectureAn event-driven workflow
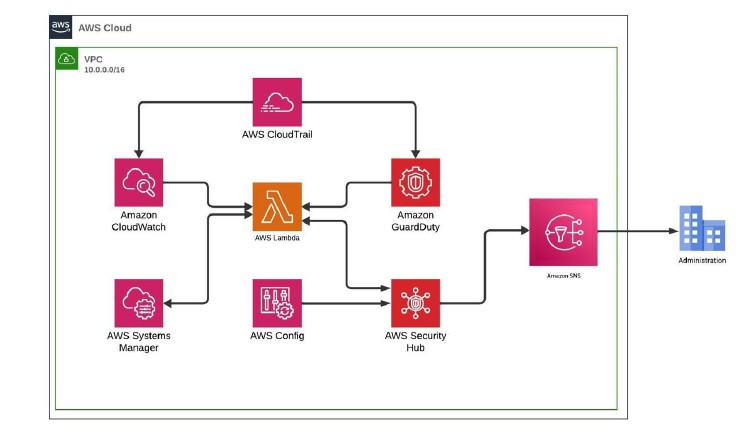
The architecture integrates multiple AWS services in an event-driven workflow:
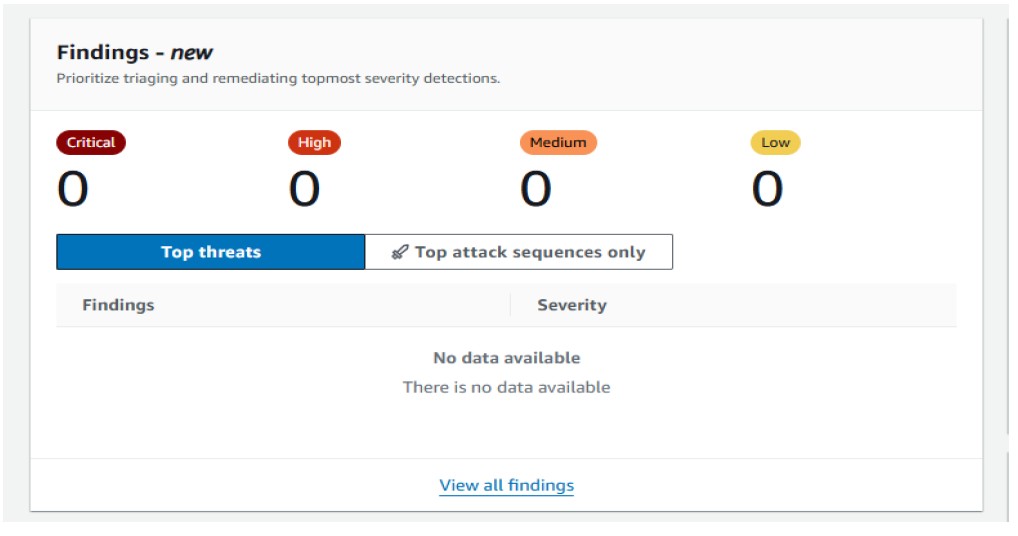
- GuardDuty for threat detection
- EventBridge for event orchestration
- Lambda for automated response actions
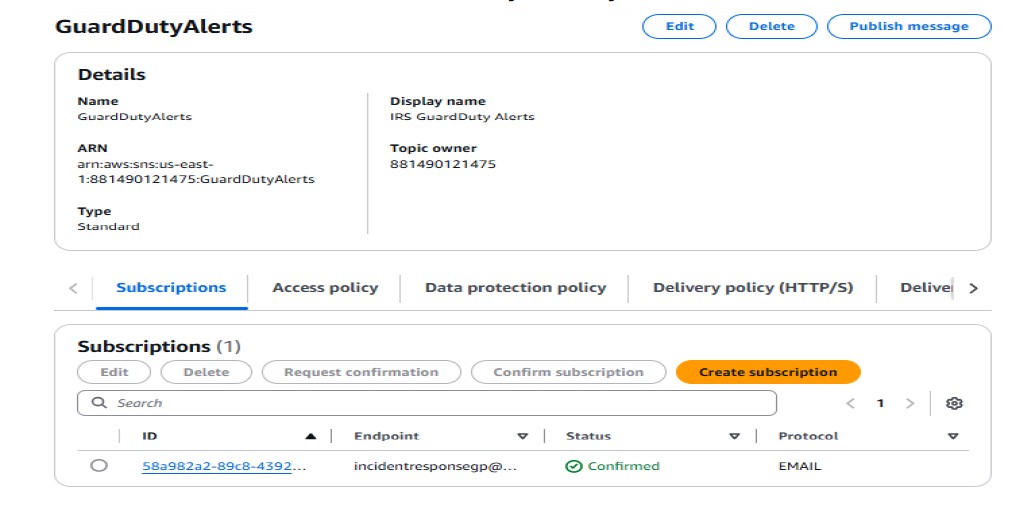
- SNS for stakeholder notifications
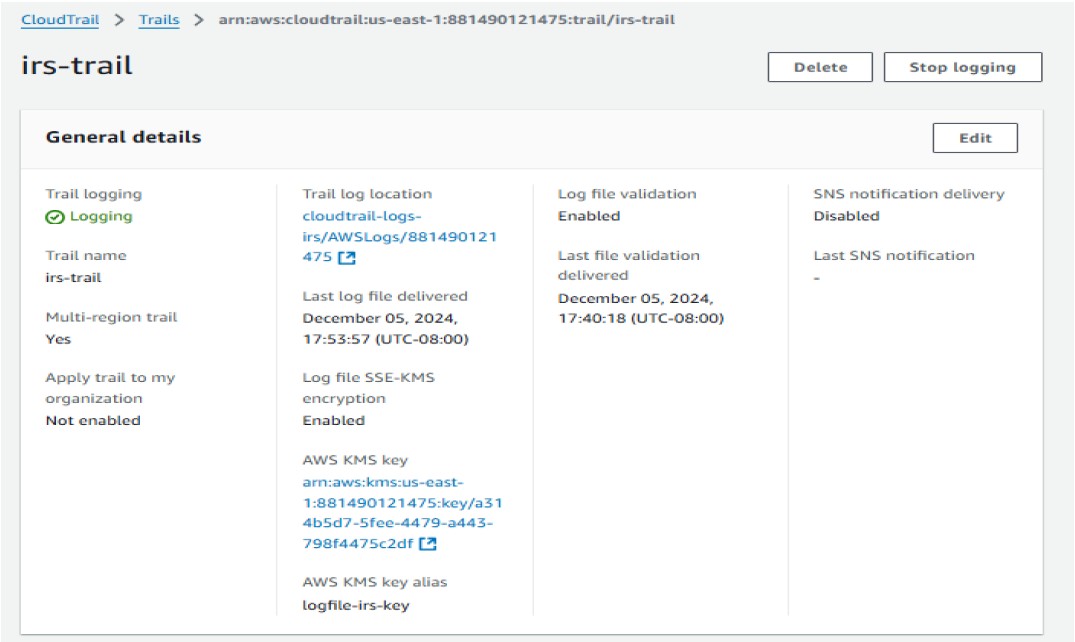
- CloudWatch & CloudTrail for monitoring and auditing
ImplementationHighlights
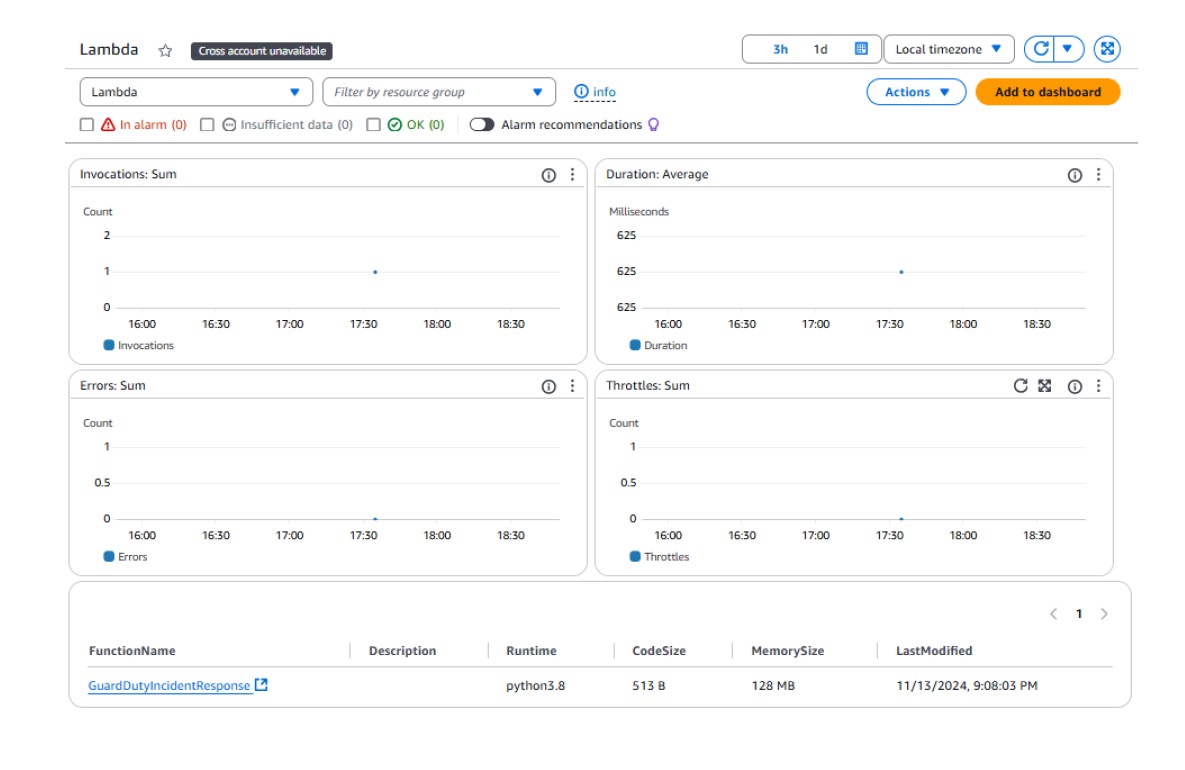
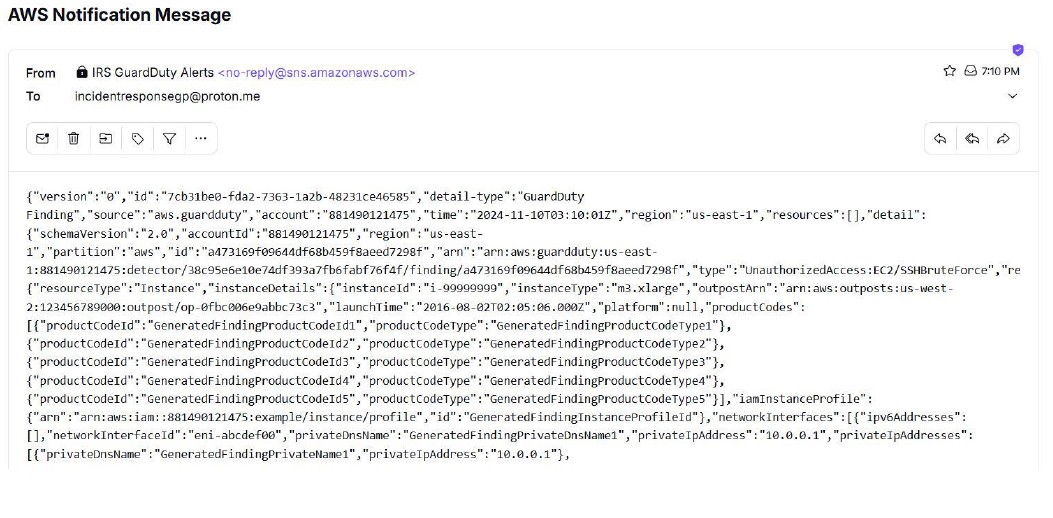
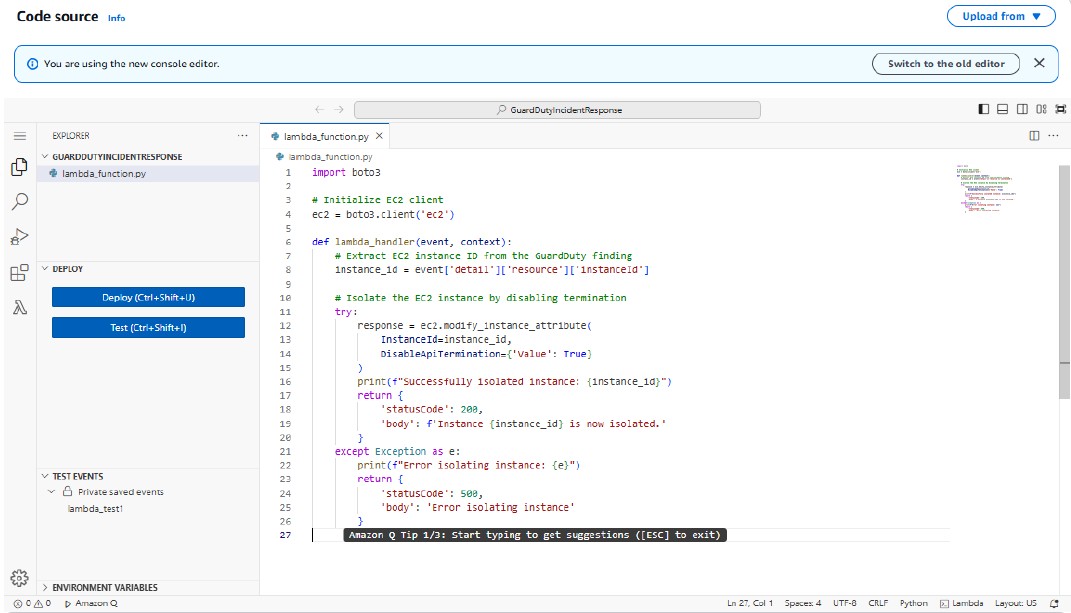
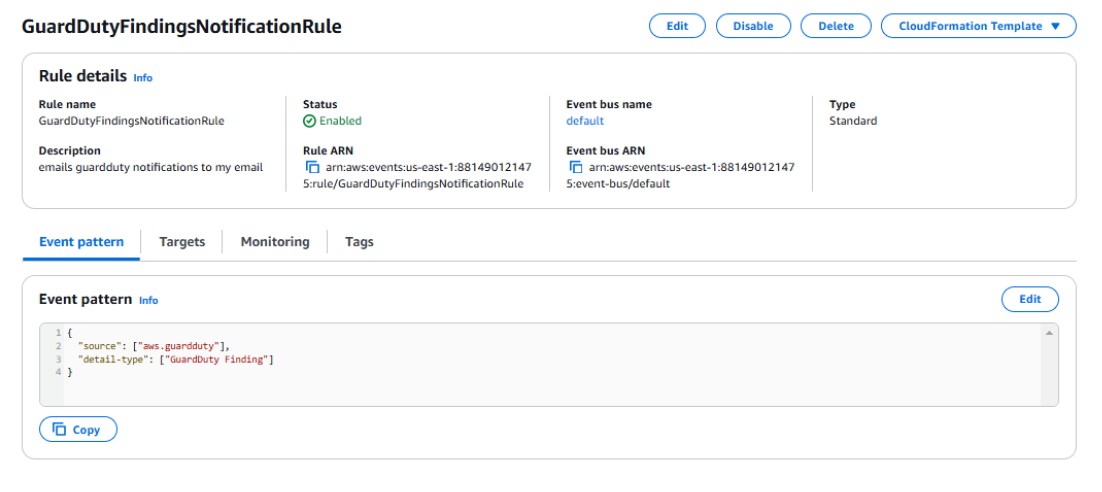
Lambda functions were developed using Python (Boto3 SDK) to automate response actions such as isolating compromised EC2 instances. EventBridge triggered these functions based on GuardDuty findings. SNS notifications were configured to alert stakeholders in real time. Click any screenshot below to enlarge it.
ValidationTesting and validation
During testing, we simulated various security incidents, including SSH brute-force attacks, port scans, and unauthorized API calls. The automated response system consistently detected these activities, triggered the corresponding Lambda functions, and promptly notified the relevant stakeholders. Each event was carefully monitored through CloudWatch logs and SNS alerts, confirming that the system executed the intended actions reliably. The response time remained within acceptable limits, demonstrating the system's effectiveness in handling security incidents with minimal delay.